Understand the record behind an assessment
Maritime Assessment Deliverables Preview
This outline shows how a scoped maritime cybersecurity assessment can organize its results for management, operations and technical staff. Actual deliverables depend on the agreed work, available evidence and authorized methods.
A record that supports the next decision
The report should make clear what was examined, what the evidence supports and what remains uncertain. Its structure should connect technical conditions with affected operations, accountable corrective actions and the evidence needed to verify a result.
Use this preview to discuss an engagement's outputs. It contains no client findings, completed assessment or regulatory compliance determination.
Scope and responsibility record
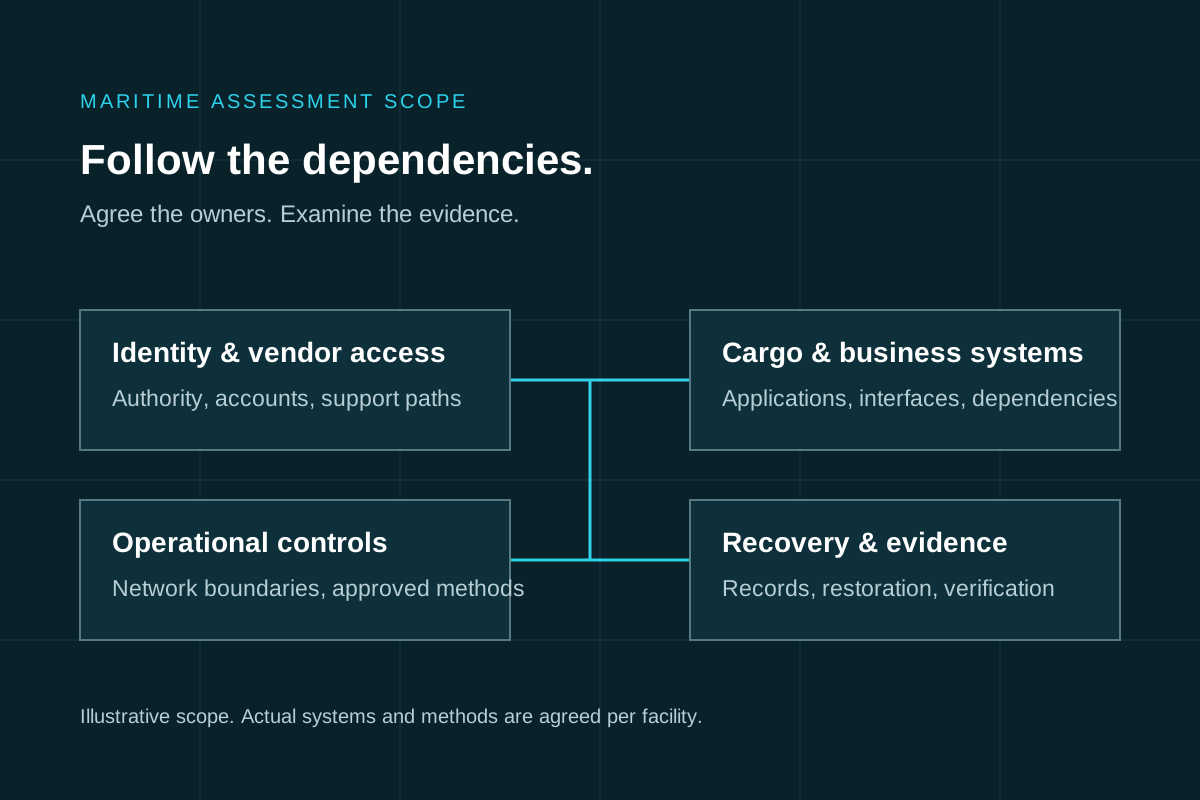
State the assessment purpose, facilities, systems, boundaries and relevant dates. Identify the owner, operator, tenants, vendors and contacts responsible for authorization and operating safeguards.
Describe the methods used, operating conditions, exclusions and untested areas. A technical workstream or gap review should be identified accurately rather than presented as a complete regulatory assessment.
- Purpose, operating boundary and responsible parties.
- Authorized methods and evidence reviewed.
- Excluded systems, third-party limits and operating constraints.
- Scope changes, evidence gaps and assessment limitations.
Asset, access and dependency record
Summarize the relevant assets, supporting IT services, communications and outside connections. Identify which records support the described relationships and where additional verification is needed.
The detail can include network boundaries, vendor-access paths, identity dependencies and systems required for selected operating functions. Restricted architecture and configuration information belongs in controlled technical material.
Findings that distinguish fact from inference
Each finding should identify the observed condition and its source, the affected systems and relevant operating consequence. Explain how a consequence was inferred and which assumptions or untested areas limit the conclusion.
A finding's severity and priority should reflect the agreed context. An unsupported pass label, unverified attack narrative or scanner output without operational interpretation should not replace the technical explanation.
- Observed condition and supporting evidence.
- Collection or review date and method, where relevant.
- Affected assets and operating dependencies.
- Reasoned consequence, uncertainty and limitations.
- Recommended next step and evidence needed for verification.
Corrective actions with ownership and verification
An action register connects each finding to a responsible owner, proposed corrective work, priority and completion evidence. It should show dependencies or operating constraints that affect scheduling.
Separate a recommended change from an implemented change and a verified result. Retesting or configuration validation can be defined as follow-up work; unresolved items remain visible.
- Finding reference and corrective objective.
- Responsible party and relevant vendor or engineering dependency.
- Priority, target date and operating conditions.
- Implementation status and supporting evidence.
- Verification criteria, results and remaining issues.
Recovery and evidence-readiness record
Document selected restoration dependencies, available backup and configuration evidence, required access, software, licensing and vendor support. If a representative recovery procedure was examined, state the conditions, result and limits of that work.
Record the relevant logging, time synchronization, isolation and preservation arrangements. Identify missing evidence and short retention periods that could limit a later incident examination. A readiness review does not establish that every system has been restored successfully.
Technical material for planning and review
Where agreed, provide a requirements-and-evidence crosswalk, technical plan-support material and an unresolved-issue register for the owner, Cybersecurity Officer and relevant advisers. State the scope of the technical contribution.
Plan authorship, filing, independent audit and regulatory approval are separate responsibilities. The crosswalk should identify evidence and gaps without certifying complete compliance or predicting approval.
Management summary and restricted technical readout
Management needs the operating implications, priorities, ownership and decisions required. Technical teams need enough controlled evidence to understand findings and perform the authorized follow-up work.
Agree the audience, handling restrictions and review process before delivery. Completion means the contracted outputs and review are finished with limitations and unresolved risks stated.
Choose the output your situation requires
An initial assessment, selected control validation and recurring assurance program need different deliverables. Bring the decision, operating boundary and existing work to a scope discussion, then agree the evidence and review needed for that purchase.