A practical planning guide for owners and operators
Prepare for a Maritime Cybersecurity Assessment
A useful assessment begins with a clear operating boundary and a question the evidence can answer. Use this guide to organize the people, records and safeguards needed to agree the work before access or testing starts.
Define the decision the assessment must support
Identify whether you need an initial assessment, an update to existing work, verification of selected corrections or a recovery review. Record relevant planning or submission dates and the advisers responsible for confirming them.
Regulatory applicability depends on the entity and operating arrangement. Establish that question with the responsible owner and advisers before treating a technical review as a complete regulatory assessment.
- What decision is due, and who will make it?
- What work already exists, and which questions remain open?
- Which findings, changes or operational dependencies require attention?
- What evidence would make the result useful to management and technical staff?
Map facilities, systems and authority
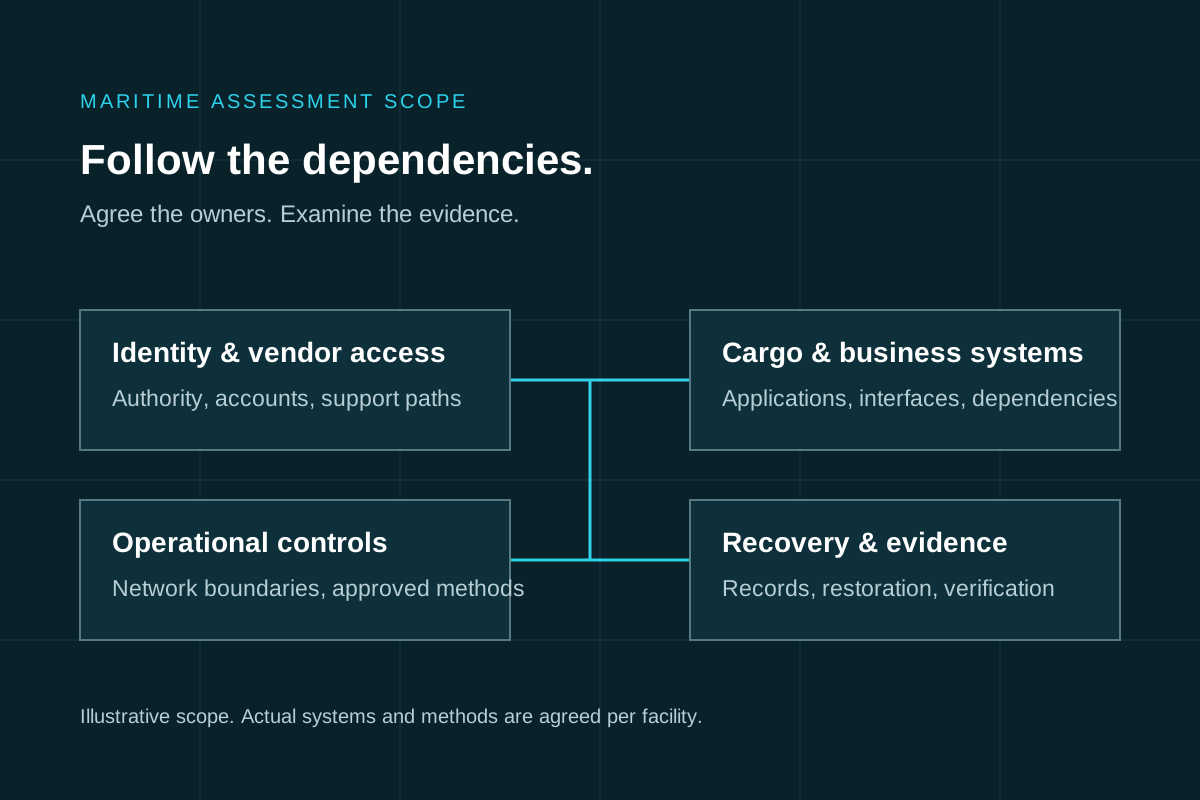
A port authority, terminal operator, tenant and equipment vendor may control different parts of the environment. Identify who owns each relevant system, who operates it and who can authorize its examination.
Include supporting business services, identity, communications and outside connections where they affect operations. A facility-wide label should not hide boundaries between separately owned or managed systems.
- General facility and operating description.
- Relevant IT/OT systems and critical operational dependencies.
- Owner, operator, tenant and vendor responsibilities.
- Access authority, excluded systems and third-party permission requirements.
Bring the people who can resolve the scope
Identify the owner or engagement sponsor, Cybersecurity Officer where applicable, security lead, operations and engineering contacts, IT administrator and relevant vendor contacts. Decide who approves methods, stops the work and receives urgent findings.
Specialist legal, regulatory or engineering responsibilities should have a named owner. Assessment work does not silently transfer those responsibilities to the technical examiner.
Inventory available records before collecting them
Prepare a list of available documents and evidence, their owners and any handling restrictions. Begin with an inventory; the initial inquiry does not require sending the records themselves.
Record gaps, approximate currency and known changes. An older diagram can still be useful when its limits are identified, but it should not be presented as the current configuration without verification.
- Asset inventory, architecture diagrams and responsibility records.
- Relevant access, identity, gateway and network-boundary configurations.
- Vendor support arrangements and remote-access approval records.
- Existing assessments, action registers and evidence of corrective work.
- Backup, restoration, software, licensing and recovery-dependency records.
- Relevant logging, time-source and incident-preservation procedures.
Set operating safeguards before any active method
Operations and engineering should identify sensitive equipment, maintenance windows, prohibited techniques, stop conditions and recovery arrangements. Define the communication path if an unexpected condition occurs.
Existing records, interviews, configuration review and approved passive evidence may answer the first questions. Any active validation requires separate approval of its target, method, timing and operating conditions. Consider representative or laboratory systems where production testing would be unsuitable.
Agree how sensitive information will be handled
Security plans, detailed architecture, credentials and incident evidence belong in an approved controlled exchange. Identify access restrictions, intended recipients, retention requirements and the rules for sharing information with vendors or other advisers.
Keep the public inquiry to general facility information, your role and the decision you need to support. Do not send Sensitive Security Information or other restricted material through a marketing form.
Agree the outputs and completion criteria
Define the systems and questions covered, methods, exclusions, deliverables, review process and client responsibilities. Distinguish an executive summary from restricted technical evidence and decide who owns each corrective action.
Completion should mean the agreed work and review are finished with limitations stated. It should not be interpreted as proof that no vulnerability exists or that a regulator has approved a plan.
- Written scope and agreed operating conditions.
- Evidence-supported findings with limitations and priorities.
- Corrective-action ownership and verification criteria.
- Management and technical readouts.
- Defined follow-up work where additional validation is needed.
Start with a non-sensitive scope discussion
Describe the facility type, general location, your role and the assessment question. Mention existing work and the people available to define operating boundaries. GDF can then discuss the appropriate technical scope and the handling arrangements for any later evidence exchange.